Trust and certifications behind Aqueduct and Milvian AI
Milvian AI holds ISO/IEC 27001 for information security management and ISO 9001:2015 for quality management, has a SOC 2 Type 2 attestation, is an AWS Advanced Tier Partner and is an NVIDIA Inception member. Aqueduct encrypts data in transit, mutually authenticates devices and cloud, uses signed tokens and role based access, logs every command and acts only with owner approval.
Certified security and quality behind a platform that acts only with your approval.
Security and quality managed to international standards
- ISO/IEC 27001
Information security is run as a certified management system with risks assessed and controls reviewed.
- ISO 9001:2015
Quality management covers how Aqueduct is designed, delivered and improved for customers.
- SOC 2 Type 2
An independent attestation reports on how security controls operated over a period of time.
Every device authenticated, every session signed
- Encrypted in transit
Device, gateway and cloud traffic is encrypted at the link and network layers.
- Mutual authentication
Gateways, devices and the cloud each prove their identity before data is accepted.
- Signed tokens
User sessions carry signed tokens tied to the organization, checked on every API call.
Owner approval first, a full record after
- Owner approval
Aqueduct acts only where control is enabled and the owner has approved it.
- Lockout protection
Lockouts hold new commands while one is executing, which protects equipment from short cycling.
- Command log
Every command is logged together with the state the device reported back afterward.
Security reviews, before and after this page
- Certifications are buried in a questionnaire weeks into procurement.
- Device security is described in vague marketing terms.
- Nobody can say who can see which data.
- Remote control of equipment feels like a black box.
- Cloud dependence rules out sensitive sites entirely.
 The Aqueduct way
- Certifications and programs are listed up front.
- Encryption and mutual authentication are stated plainly.
- Role based access scopes every user and tenant.
- Every command needs approval and is logged.
- On-prem deployment keeps sensitive data on site.
What Milvian AI holds
Ask for certificates and reports during procurement.
ISO/IEC 27001
Certified information security management system covering how we protect information and manage security risk.
ISO 9001:2015
Certified quality management system for how we design, deliver and improve our work.
SOC 2 Type 2
Independent attestation that our security controls were designed well and operated effectively over a period of time.
AWS Advanced Tier Partner
Aqueduct runs on AWS, and Milvian AI is an AWS Advanced Tier Partner.
NVIDIA Inception member
Milvian AI is a member of the NVIDIA Inception program. Aqueduct runs on-prem AI on NVIDIA infrastructure.
Platform security
Encryption, authentication, access control and command safeguards, described in full on the security page.
Learn moreHow Aqueduct protects data and equipment
Product facts from the Aqueduct architecture.
| Area | How Aqueduct handles it |
|---|---|
| Encryption in transit | Device to gateway to cloud communications are encrypted at the link and network layers; the web application is served over HTTPS |
| Device identity | Mutual authentication between gateways, devices and the cloud, so each endpoint proves who it is |
| User sign-in | Users sign in and receive signed JWT tokens tied to their organization |
| Access control | Role based access scopes what each user sees, down to tenant shares on a shared meter |
| API protection | Public APIs require a valid signed token; internal APIs require cloud identity credentials |
| Control safeguards | Control only where enabled, with owner approval; lockouts prevent short cycling |
| Audit trail | Every command is recorded in a command log, with the device's reported state confirming execution |
| Deployment choice | AWS cloud, or on-prem with on-prem AI on NVIDIA infrastructure for data that must stay on site |
From device to decision, securely
Every hop is authenticated and every command is recorded.
Sense
Sensors, meters and equipment report through LoRaWAN or IP gateways and a field device network controller.
Transmit
Gateways send data over Ethernet, Wi-Fi or LTE, encrypted and mutually authenticated.
Store and analyze
Data lands in AWS IoT Core and managed AWS time series and database services, scoped to your organization.
Act with approval
Commands run only where control is enabled with owner approval, through queued commands and device shadows.
Record
The command log keeps every command and its result for audit and for measurement and verification.
What our certifications cover, and what they do not
ISO/IEC 27001, ISO 9001:2015 and SOC 2 Type 2 describe how Milvian AI runs its own information security and quality management. They are about us and the way we build and operate Aqueduct.
They do not certify your buildings, and Aqueduct does not make a building compliant with any standard. For energy, water and air standards, Aqueduct supplies measured evidence and your team or consultant files. See the compliance section for how that works.
Trust at a glance
Certifications, programs and safeguards.
Security at a glance
What the product does, stated plainly.
Encrypted and authenticated
Device, gateway and cloud traffic is encrypted at the link and network layers, with mutual authentication between endpoints.
Signed tokens and roles
Users sign in with signed tokens tied to their organization, and role based access scopes what each user sees.
Owner approval for control
Aqueduct acts only where control is enabled and never without owner approval. Lockouts prevent short cycling.
Auditable command log
Every command is recorded, and the device's reported state confirms whether it executed.
Cloud or on-prem
Run on AWS, or on your premises with on-prem AI on NVIDIA infrastructure for data that cannot leave.
Certified organization
ISO/IEC 27001, ISO 9001:2015, SOC 2 Type 2, AWS Advanced Tier Partner and NVIDIA Inception member.
Learn more
Security posture by layer
From the device in the ceiling to the person in the browser.
| Layer | Safeguard |
|---|---|
| Devices and gateways | Encrypted at the link and network layers; mutual authentication between endpoints; optional independent LTE backhaul that avoids the customer network |
| Ingest | Data enters through AWS IoT Core topic rules, is decoded per vendor and model, and is mapped to the right asset |
| Storage | Time series and entity data held in managed AWS services, scoped by organization |
| Application | Served over HTTPS through a content delivery network; sign-in issues signed JWT tokens |
| APIs | Public APIs require a valid signed token; internal APIs require cloud identity credentials |
| Access | Role based access; on shared meters, landlords see totals and shares while tenants see only their own share |
| Control | Command queues, device shadows with desired and reported state, lockouts, owner approval and a command log |
| Certifications | ISO/IEC 27001, ISO 9001:2015 and SOC 2 Type 2, with documents shared during procurement |
How control stays safe
Acting is part of the flywheel. So is proving the action was safe and real.
Enabled
Control is switched on only for the devices and sites where the owner wants it.
Approved
Aqueduct does not take control without owner approval.
Protected
Lockout warnings hold new commands while one is still being acted on, which prevents short cycling.
Confirmed
The device reports its state back, and the command log records whether the command executed.
Verified
The meter confirms the result. Every verified result becomes the new baseline.
What security reviews ask
Facilities and infrastructure data is operational data. The questions are fair.
Where does the data go?
To AWS, or nowhere outside your site if you deploy on-prem. Hosting details are shared during procurement.
Can software move my equipment?
Only where control is enabled and with owner approval. Lockouts stop commands stacking up on a unit.
Who can see what?
Role based access scopes each user, and tenants on a shared meter see only their own share.
Can I prove what happened?
The command log shows every command and whether it executed, which matters for audits and M&V.
Questions by seat
“Can I see and stop what the platform does to my equipment?”
Control runs only where you enable and approve it, and every command is in the log.
“Does my network data have to leave my control room?”
No. Deploy on-prem. For networks, Aqueduct reads data alongside SCADA, and control stays with SCADA.
“What will my client's security team ask, and where are the answers?”
Encryption, authentication, access and control safeguards are on this page. Certificates and the SOC 2 Type 2 report come during procurement.
Certifications and programs
Held by Milvian AI. Details on the trust page.
Where teams put it to work
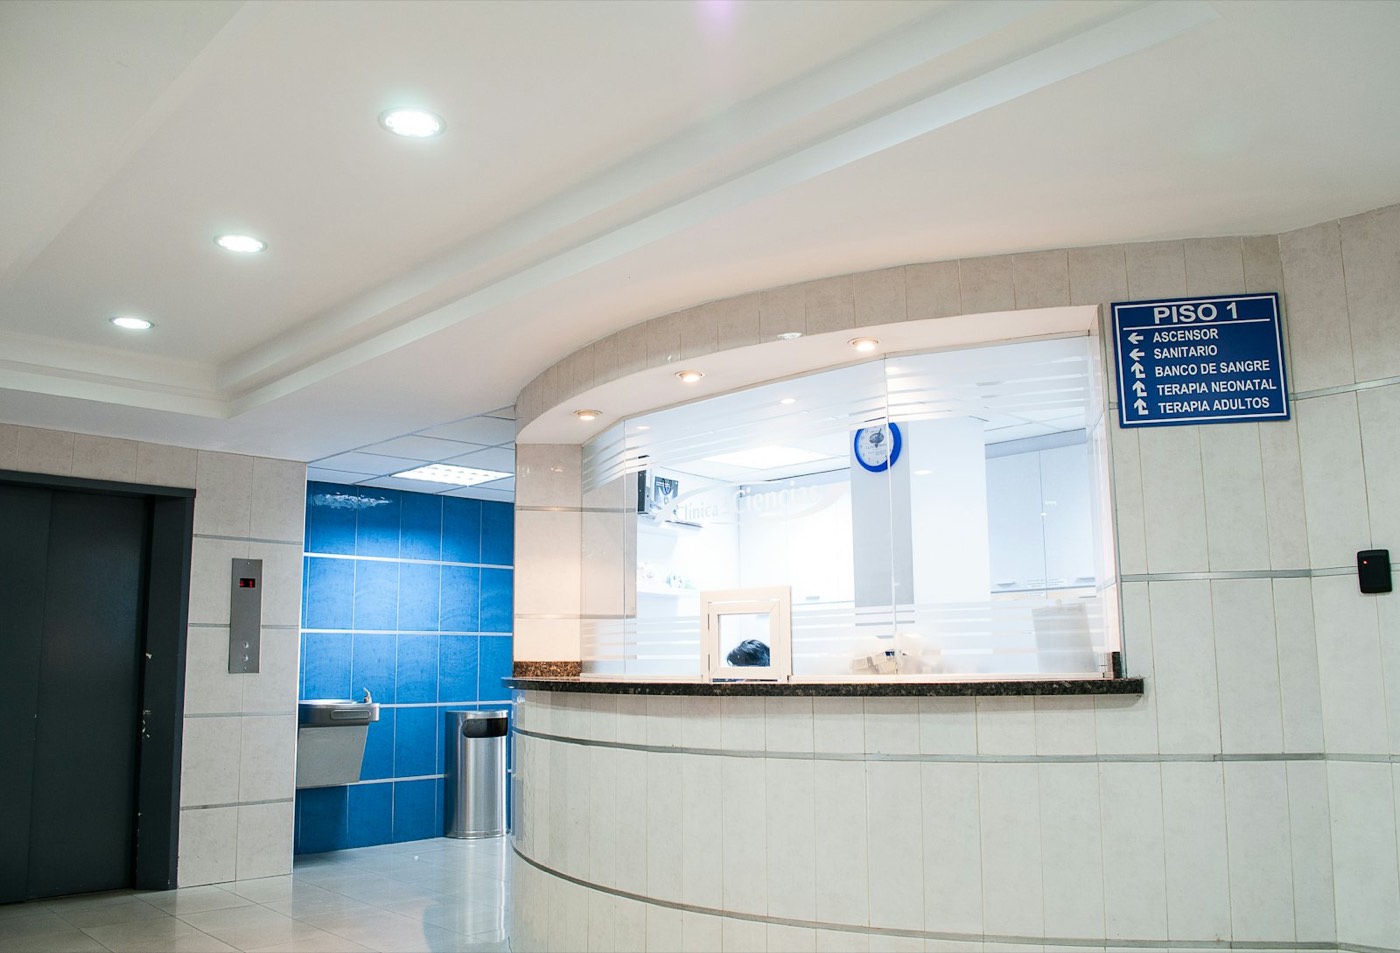
Security reviews for clinical sites
Hospital IT teams review certifications, access control and on-prem options before any device joins the network. This page answers the first questions.
Learn more
Data that stays on premises
Public sector sites that cannot send data out can run Aqueduct on-prem, with on-prem AI on NVIDIA infrastructure.
Learn more
Certificates ready for vendor review
Procurement teams receive ISO certificates and the SOC 2 Type 2 report early, so vendor review runs alongside scoping.
Learn moresites in 21 countries run on Aqueduct.
and 9 clinics in one of India’s top hospital chains.
US airport running water intelligence on Aqueduct.
of commercial real estate under Aqueduct.
FMCG manufacturing campus.
operations run on Aqueduct.
Related
Common questions
Yes. Milvian AI holds ISO/IEC 27001 certification for its information security management system, which covers how Aqueduct is built and operated. Certificates are available during procurement.
Yes. Milvian AI has a SOC 2 Type 2 attestation, which reports on how its security controls operated over a period of time, including for Aqueduct. The report is shared during procurement.
Yes. Milvian AI holds ISO 9001:2015 certification for its quality management system, covering how Aqueduct is designed, delivered and improved.
Yes. Milvian AI is an AWS Advanced Tier Partner, and Aqueduct runs on AWS. Aqueduct is also available through AWS Marketplace.
Milvian AI is a member of the NVIDIA Inception program. Aqueduct can run on-prem AI on NVIDIA infrastructure for sites where data must stay on premises.
Communications from devices through gateways to the cloud are encrypted at the link and network layers, and endpoints use mutual authentication. Aqueduct's web application is served over HTTPS.
No. Milvian AI's certifications cover its own security and quality management. Aqueduct supplies measured evidence for building standards, and your team or consultant files and certifies.
Aqueduct gateways encrypt communications at the link and network layers and use mutual authentication between endpoints. Data then enters the cloud through authenticated device connections.
No. Aqueduct acts only where control is enabled and never takes control without owner approval. Lockouts prevent short cycling, and every command is logged.
Aqueduct records every command in the command log, and the device's reported state confirms whether it executed. That record supports audits and measurement and verification.
See Aqueduct on your own facility.
Bring a site, a utility bill or a question. We will show you where the loss is.